 NeoBit Daily
Introduction to Cybersecurity Challenges in Satellite Constellations
As satellite constellations expand rapidly in 2026, protecting orbital infrastructure from sophisticated cyber threats has become a critical priority for governments, commercial operators, and global communications networks. Satellite systems now underpin everything from GPS navigation to broadband internet and military operations, making them high-value targets. This article examines rising threats, documented attack vectors such as data interception and jamming, and advanced mitigation approaches including encryption protocols and real-time anomaly monitoring. The growth of mega-constellations with thousands of interconnected satellites creates an expanded attack surface that demands specialized defenses beyond traditional IT security models.
Building on established space security practices, we analyze practical defense frameworks that security teams can implement immediately. The focus remains on advanced techniques and regulatory compliance to help professionals safeguard these assets effectively. With increasing reliance on low-Earth orbit networks for everyday services, understanding these risks is essential for maintaining resilient global infrastructure.
Key Cybersecurity Threats Facing Satellite Networks in 2026
Satellite constellations operate in a unique environment where traditional terrestrial defenses often fall short. Primary threats include signal jamming, data interception during uplink and downlink transmissions, and supply-chain compromises in ground stations. Attackers increasingly leverage AI-driven tools to identify vulnerabilities in constellation handoffs between satellites, allowing for precise targeting of specific orbital assets.
Another growing concern involves spoofing attacks that mimic legitimate satellite signals, potentially disrupting services for millions of users. These threats are amplified by the sheer number of low-Earth orbit satellites, which increases the attack surface dramatically. Additional risks stem from insider threats at ground control facilities and ransomware targeting satellite command software. As constellations become more autonomous, vulnerabilities in onboard firmware and inter-satellite links represent emerging attack vectors that require constant vigilance.
Real-World Attack Cases: Data Interception and Jamming
Documented incidents highlight the severity of these risks. In one notable case, adversaries intercepted sensitive telemetry data from a commercial constellation, exposing operational parameters and allowing competitors to gain strategic insights. Jamming attacks have also targeted specific frequency bands, temporarily disabling services across wide geographic areas and affecting emergency response communications. Such examples underscore the need for layered defenses rather than reliance on any single technology. Recent simulations have shown how coordinated jamming combined with spoofing can create cascading failures across multiple satellite operators.
Mitigation Strategies: Encryption and Anomaly Monitoring
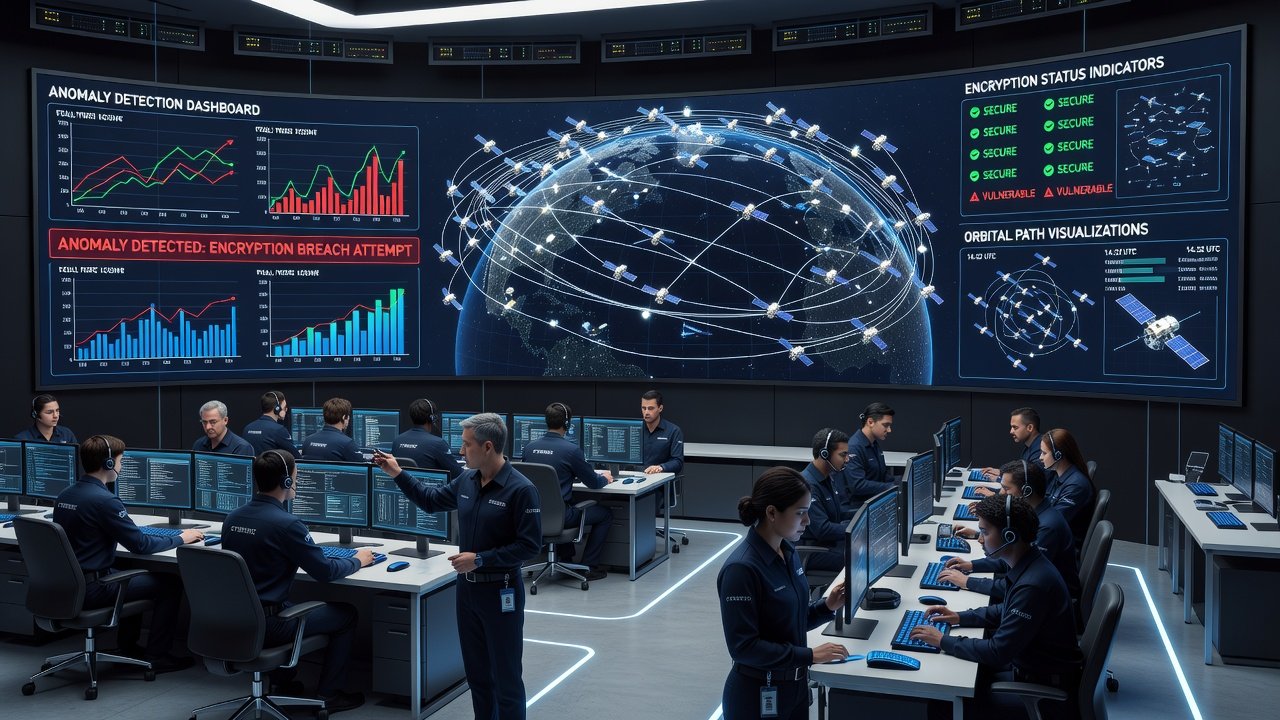
Effective protection starts with robust end-to-end encryption for all satellite communications. Quantum-resistant algorithms are gaining traction to future-proof against emerging decryption capabilities, ensuring long-term data confidentiality. Complementing encryption, continuous anomaly monitoring uses machine learning models to detect deviations in signal patterns or orbital behavior in real time, enabling proactive responses before disruptions escalate.
Operators should integrate these tools with ground-based security operations centers for rapid response. Regular penetration testing of both space and ground segments further strengthens resilience. Additional techniques include implementing secure boot processes for satellite firmware and deploying honeypots within network architectures to divert and study potential attackers. Multi-layered authentication for command signals adds another critical barrier against unauthorized access attempts.
Comparing Defense Tools for Satellite Cybersecurity
When evaluating solutions, teams often compare commercial offerings against open-source frameworks. Key factors include integration with existing satellite command systems, scalability across large constellations, and support for compliance standards. Tools emphasizing behavioral analytics tend to outperform signature-based approaches in dynamic orbital environments. For instance, platforms with advanced AI correlation engines provide faster detection of subtle jamming attempts compared to legacy systems. Cost-effectiveness, ease of deployment across heterogeneous satellite fleets, and vendor support for emerging threats also play major roles in selection decisions. Teams should conduct proof-of-concept trials to assess real-world performance under simulated attack conditions.
Practical Checklist for Security Teams
Developing a thorough security program requires systematic steps. Begin by conducting comprehensive asset inventories of all satellites, ground stations, and communication links to identify every potential entry point. Implement multi-factor authentication and zero-trust architectures for all access points to minimize unauthorized entry risks. Deploy encryption standards aligned with current NIST guidelines to protect data integrity across transmissions.
Establish 24/7 anomaly detection with automated alerting to enable immediate investigation of suspicious activities. Perform quarterly tabletop exercises simulating jamming and interception scenarios to test response protocols and team readiness. Review and update incident response plans to include orbital-specific recovery procedures, such as satellite repositioning or frequency hopping. Additional checklist items include regular supply chain audits for hardware components and mandatory security training for all personnel involved in satellite operations.
Privacy Implications for Global Communications
Beyond technical defenses, satellite cybersecurity directly affects user privacy. Intercepted communications can reveal sensitive location data or corporate intelligence, leading to potential espionage or identity theft on a massive scale. Organizations must balance operational security with privacy regulations, ensuring data handling practices comply with international frameworks. The interconnected nature of constellations means a single breach could expose data from users worldwide, raising complex questions about jurisdiction and data sovereignty. Implementing privacy-by-design principles during constellation development helps mitigate these long-term risks while maintaining service functionality.
Compliance and Regulatory Considerations
Security leaders should align with guidelines from authoritative bodies. Resources from NASA and ESA provide valuable frameworks for orbital security. Additionally, consulting CISA recommendations helps address critical infrastructure protections applicable to satellite networks. Staying current with evolving international standards ensures organizations avoid penalties and maintain operational licenses. Regular audits against these benchmarks also demonstrate due diligence to stakeholders and partners.
Advanced Techniques and Future Outlook
Looking ahead, integration of blockchain for secure satellite command logging offers promising tamper-proof audit trails. Collaborative threat intelligence sharing among operators can accelerate identification of new attack patterns. As 2026 progresses, investment in resilient constellation designs with redundant pathways will become standard practice for forward-thinking organizations.
Conclusion
Securing satellite constellations in 2026 requires a proactive, multi-layered strategy combining encryption, monitoring, and rigorous compliance. By learning from past incidents and applying structured checklists, security professionals can mitigate risks effectively and protect vital global infrastructure for years to come.
Targeted FAQs for Security Professionals
What are the most common attack vectors on satellite constellations?
Jamming, signal interception, and ground-station compromises remain the leading vectors, often combined in coordinated campaigns that exploit both space and terrestrial components.
How does encryption protect satellite communications?
End-to-end encryption secures data in transit, preventing unauthorized access even if signals are intercepted during transmission phases.
Which monitoring techniques are most effective for anomaly detection?
Machine learning-based behavioral analytics outperform traditional methods by identifying subtle deviations in real time across vast data streams from multiple satellites.
Are there specific compliance standards for orbital cybersecurity?
Aligning with NIST, NASA, and CISA guidelines provides a strong foundation for regulatory adherence and operational best practices.
How can teams prepare for supply-chain attacks in satellite hardware?
Conducting rigorous vendor assessments and implementing hardware attestation protocols during manufacturing and deployment phases reduces exposure significantly.
No comments yet. Be the first!