 NeoBit Daily
Introduction to Deception Technology in 2026
Deception technology has emerged as a proactive layer in modern cybersecurity, shifting the advantage from attackers to defenders. In 2026, organizations face increasingly sophisticated threats that traditional perimeter defenses struggle to contain. By deploying realistic decoys such as honeypots, honeytokens, and entire decoy networks, security teams can detect intrusions early, gather threat intelligence, and safeguard sensitive data privacy. This approach not only delays attackers but also provides actionable insights that improve overall resilience. As ransomware groups and state-sponsored actors refine their techniques, deception offers a dynamic countermeasure that adapts to evolving attack patterns without requiring constant signature updates.
Deception works by creating an environment where attackers waste time and resources on false targets, revealing their tactics without compromising real assets. As cyber threats evolve, integrating these tools with existing security infrastructure becomes essential for compliance and risk reduction. Organizations that adopt deception early often report higher confidence in their ability to meet data protection mandates.
Understanding Honeypots and Their Role in Data Protection
Honeypots are decoy systems designed to mimic production environments. They lure attackers into interacting with fake assets, allowing defenders to monitor behavior in real time. Low-interaction honeypots simulate basic services with limited functionality, making them quick to deploy but easier for sophisticated attackers to identify. High-interaction honeypots run full operating systems and applications to capture deeper attack details, though they demand more maintenance and carry slightly higher risk if not properly isolated. In 2026, these tools are particularly valuable for protecting data privacy by isolating potential breaches and preventing lateral movement toward genuine databases or customer records.
Deployment begins with identifying high-value assets and placing honeypots in strategic network segments. This setup helps organizations comply with privacy regulations by minimizing the attack surface around real data stores. For instance, a retail company might position honeypots near payment processing systems to divert attention from actual transaction databases.
Honeytokens: Lightweight Decoys for Early Detection
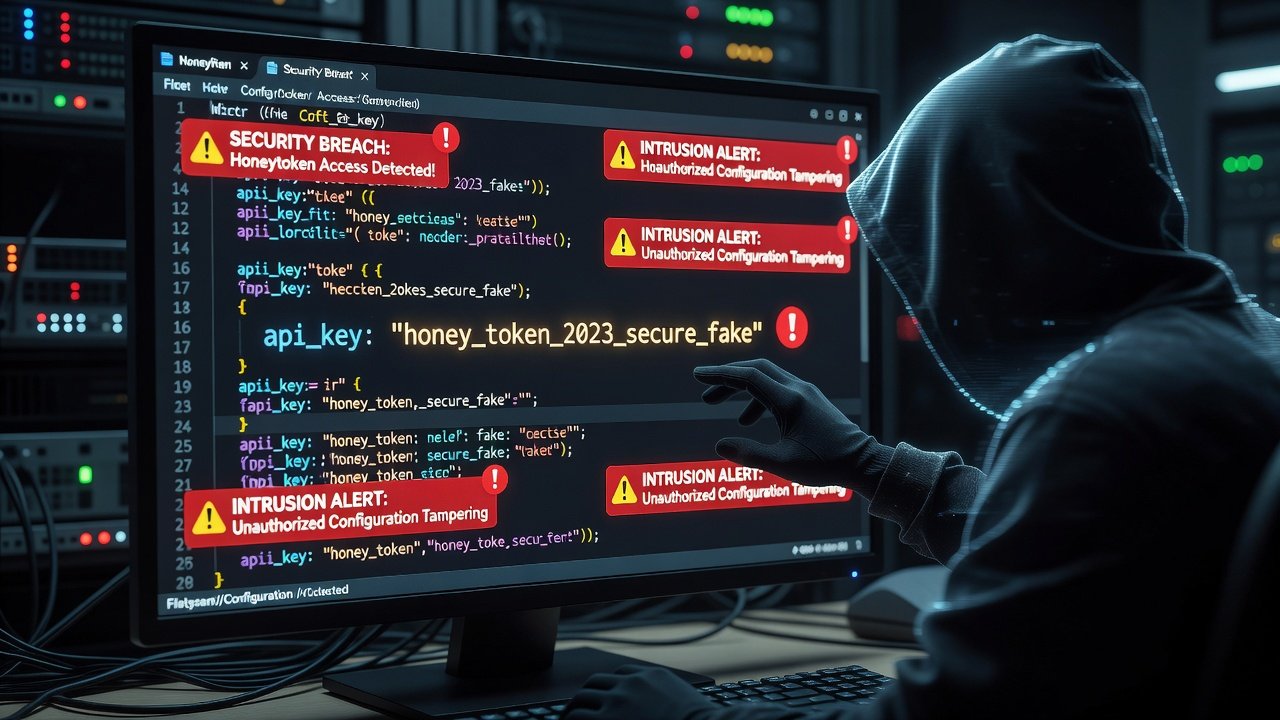
Honeytokens are digital breadcrumbs such as fake credentials, API keys, or database entries that trigger alerts when accessed. Unlike full honeypots, they require minimal resources yet deliver high-fidelity signals of compromise. For example, embedding a honeytoken in a configuration file can immediately notify teams if an attacker attempts to exfiltrate information, directly supporting data privacy objectives by enabling rapid response before sensitive records are exposed. Security teams often combine honeytokens with behavioral analytics to distinguish legitimate access from malicious activity, reducing false positives that plague traditional monitoring.
Practical applications include placing honeytokens in source code repositories or cloud storage buckets. When an unauthorized query occurs, the system logs the IP address, timing, and attempted actions, giving analysts immediate context for investigation.
Decoy Networks and Their Strategic Value
Decoy networks extend the deception concept across entire segments, creating realistic replicas of production infrastructure. These networks can include simulated servers, endpoints, and even user traffic patterns generated through virtualization technologies. When integrated into a broader strategy, decoy networks help organizations map attacker kill chains and strengthen defenses around privacy-critical systems. Recent implementations show that decoy networks reduce dwell time by an average of 60 percent, allowing teams to contain threats before data exfiltration occurs.
Advanced decoy networks now incorporate machine learning to dynamically adjust their appearance based on observed attacker behavior, making them harder to distinguish from legitimate environments.
Deployment Strategies for Effective Implementation
Successful deployment requires careful planning. Start by conducting a risk assessment to prioritize assets that need protection. Next, select deception tools that align with your environment—whether cloud-native or on-premises. Gradual rollout with monitoring phases ensures minimal disruption. Integration points should include network segmentation to isolate decoys and automated response playbooks triggered by alerts. Teams should also establish clear policies for handling captured attacker data while respecting privacy laws. Additional considerations include regular updates to decoy configurations to prevent attackers from recognizing static patterns and conducting tabletop exercises to test response procedures.
Organizations should evaluate vendor solutions for scalability and ease of management, ensuring the chosen platform supports both on-premise and hybrid cloud deployments common in 2026 environments.
Integration with SIEM and Behavioral Analytics
Deception technology delivers maximum value when connected to Security Information and Event Management (SIEM) platforms and behavioral analytics engines. Alerts from honeypots and honeytokens feed directly into SIEM dashboards, enriching existing logs with high-confidence indicators of compromise. Behavioral analytics then correlate these signals with user activity to identify anomalies faster. This integration creates a closed-loop system where deception data continuously trains detection models, improving accuracy over time. Organizations following NIST guidelines often achieve stronger outcomes by aligning deception feeds with established cybersecurity frameworks.
Further benefits arise when deception outputs are combined with user and entity behavior analytics (UEBA) tools. For example, a sudden spike in access attempts to a honeytoken can trigger automated quarantines, limiting potential damage while analysts review the incident.
Real-World Case Studies and Measurable Outcomes
A global financial services firm deployed honeytokens across its cloud environments and reduced successful credential-stuffing attempts by 75 percent within six months. Another healthcare provider used a decoy network to detect an advanced persistent threat early, preventing exposure of patient records and maintaining compliance with privacy standards. A third example comes from a manufacturing company that integrated honeypots with its SIEM; the result was a 50 percent faster mean time to detect (MTTD) and improved audit readiness for regulatory reviews.
These examples demonstrate measurable benefits including faster incident response and reduced regulatory risk. According to industry reports referencing CISA resources, organizations leveraging deception see an average 40 percent improvement in threat visibility. Qualitative gains include higher team morale as analysts shift from reactive firefighting to strategic threat hunting.
Common Mistakes to Avoid
Many teams overlook the need for ongoing maintenance, allowing decoys to become outdated and easily spotted by attackers. Another frequent error is failing to tune alert thresholds, which leads to alert fatigue. Security leaders should also avoid placing decoys too close to production systems without proper isolation, as this can inadvertently increase risk rather than reduce it.
Practical Checklist for Security Teams
- Map critical data assets and identify privacy-sensitive areas
- Select appropriate deception tools based on environment scale and cloud compatibility
- Deploy honeypots and honeytokens in low-traffic segments first, then expand gradually
- Connect deception alerts to SIEM and behavioral analytics platforms with automated playbooks
- Establish response playbooks and train analysts on decoy alerts through simulated scenarios
- Review and update decoys quarterly to maintain realism and relevance
- Measure key metrics such as time-to-detect, attacker engagement duration, and false positive rates
- Ensure all deception activities align with data privacy regulations and conduct periodic audits
- Document lessons learned after each simulated or real incident to refine future deployments
Frequently Asked Questions
How does deception technology impact legitimate users?
Properly implemented deception remains invisible to authorized personnel. Decoys are placed outside normal workflows, and alerts are tuned to ignore routine activity, ensuring no disruption to daily operations.
What skills are required to manage honeypots and honeytokens?
Teams need basic networking knowledge and familiarity with SIEM tools. Many vendors provide managed services that reduce the learning curve, allowing smaller teams to benefit without extensive in-house expertise.
Can deception technology replace traditional security controls?
No. It serves as a complementary layer that enhances detection and response when used alongside firewalls, endpoint protection, and access controls. It should never be viewed as a standalone solution.
How does deception support regulatory compliance?
By providing detailed logs of attacker interactions, deception helps demonstrate due diligence in protecting personal data, supporting frameworks such as GDPR and CCPA through evidence of proactive monitoring.
Conclusion
Deception technology, encompassing honeypots, honeytokens, and decoy networks, offers a powerful way to strengthen cybersecurity and protect data privacy in 2026. By following structured deployment strategies and integrating with SIEM and analytics platforms, security teams gain early visibility into threats while minimizing risk to real assets. The practical checklist, expanded FAQ, and guidance on avoiding common mistakes provided here equip organizations to begin implementation confidently and achieve lasting improvements in their security posture. As the threat landscape continues to shift, deception remains a forward-looking investment that delivers both immediate detection gains and long-term strategic advantages.
No comments yet. Be the first!